◈
Critical
Active exploit attempts, ransomware behavior, or privilege escalation in production workloads.
◷ Block immediately
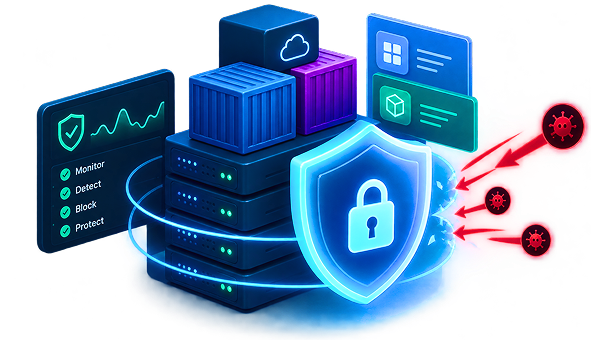
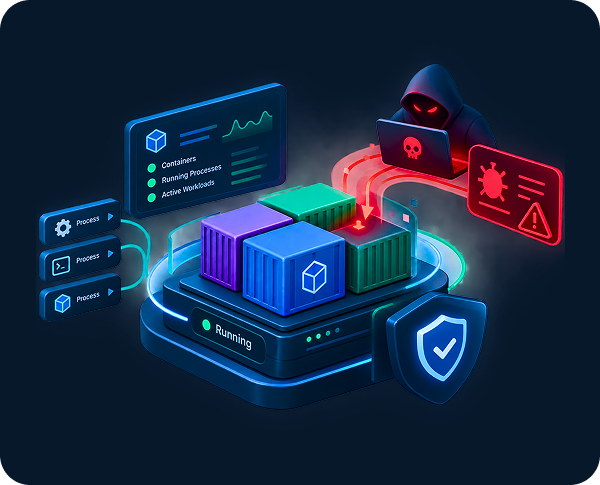
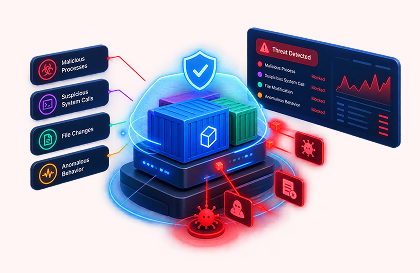
Identify malicious processes, suspicious system calls, file changes, and anomalous behavior as workloads run.
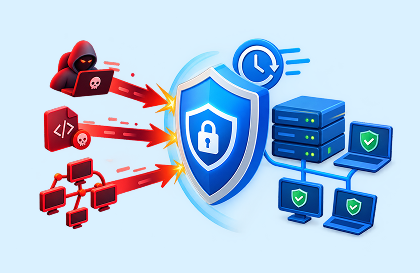
Stop exploit attempts, unauthorized process execution, and lateral movement before damage spreads.
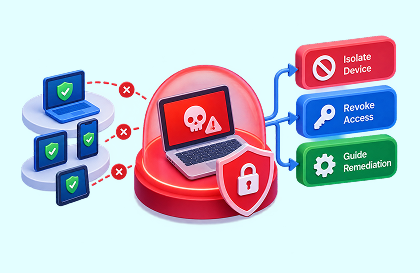
Isolate compromised workloads, kill malicious processes, and guide rapid remediation with clear context.
Prioritized by threat severity, workload criticality, and potential blast radius — so teams stop the most dangerous runtime risks first.
Active exploit attempts, ransomware behavior, or privilege escalation in production workloads.
Suspicious process chains, unexpected network connections, or unauthorized container activity.
Policy deviations, unusual runtime patterns, or non-critical anomalies that need review.
Live output from MadStack Runtime Protection — exact workload, threat type, and recommended action.
It continuously monitors running workloads, containers, and applications to detect malicious processes, exploit attempts, unauthorized changes, and anomalous behavior in real time.
Vulnerability scanning finds known weaknesses before or during deployment. Runtime Protection defends live systems against attacks and suspicious behavior that only appear while workloads are running.
Yes. You can configure policies to automatically kill malicious processes, isolate compromised workloads, and trigger response workflows when critical threats are detected.