Services›Code›Secret Detection
Stop leaks before they happen.

Secret Detection

Find exposed API keys, tokens, passwords, and credentials in your code — before they reach production or public repos.
Secret Detection
Secrets leaking from code
The problem

Secrets leak more often than you think.

Developers accidentally commit API keys, database passwords, and cloud tokens every day. Once in git history or a public repo, they’re almost impossible to fully remove. Traditional scanners miss custom secrets and lack context — leaving your organization exposed.
One operating picture

One scan. Complete visibility.

MadStack scans your entire codebase, history, and PRs to detect both known and custom secrets — with high accuracy and almost zero noise.
Detect all secrets

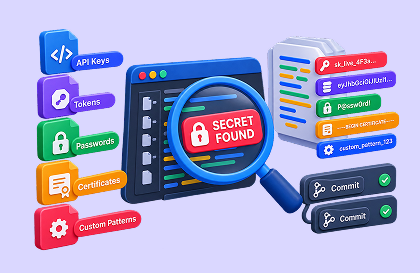
Detect all secrets

Find API keys, tokens, passwords, certificates, and custom patterns across every file and commit.

Smart context analysis

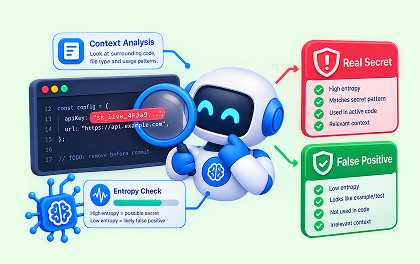
Smart context analysis

Understand whether a string is a real secret or just a false positive using surrounding code and entropy.

Block before exposure

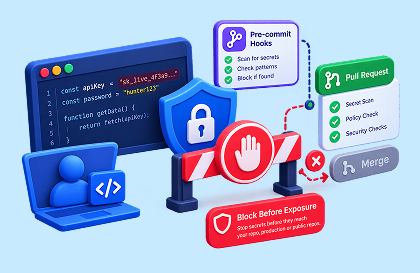
Block before exposure

Prevent secrets from being committed or merged with real-time PR checks and pre-commit hooks.

✦ What gets detected

Findings, ranked by what matters.

Prioritized by secret type, exposure risk, and whether the credential is still active — so you fix the most dangerous leaks first.

◈

Critical

Live production secrets (cloud keys, database credentials, private keys) that are currently exposed.

◷ Rotate immediately
!

High

Valid secrets in recent commits or PRs that haven’t been rotated yet.

◷ Revoke & remove
↗

Medium

Test secrets, expired tokens, or low-risk credentials that still shouldn’t be in the repo.

◷ Clean up soon
Sample finding

Evidence your team can act on.

Live output from the MadStack scanner — exact file, secret type, and recommended action.
File
aws.ts
Issue
AWS Access Key (Active)
src/config/aws.ts
{
"file": "aws.ts",
"line": 18,
"secret_type": "AWS Access Key",
"status": "Active",
"action": "Rotate key & remove from git history"
}
FAQ illustration
FAQ

Questions, answered.

Most tools only look for known patterns and generate lots of false positives. MadStack uses entropy + context analysis to find both known and custom secrets with much higher accuracy.

Yes. We scan the full git history so even secrets that were committed months ago and later removed can still be detected and cleaned up.

Absolutely. You can enable pre-commit hooks and PR checks that block any commit or merge containing secrets.
More in Code

Explore More Security Topics

Dive deeper into specific areas of application security, from source code analysis to dependency risks and beyond.
SAST

SAST

Find and fix security flaws in your source code before they ship.

Deep PR Review

Deep PR Review

AI-powered code review for deeper, faster, and smarter security.

Code Quality

Code Quality

Detect complexity, code smells, and technical debt early.

Ready when you are

Stop secret leaks. Before they spread.

Secret Detection CTA