Services›Code›SAST
Advanced AppSec suite, built for devs.

SAST — Static Application Security Testing

Find insecure code before it ever reaches production.
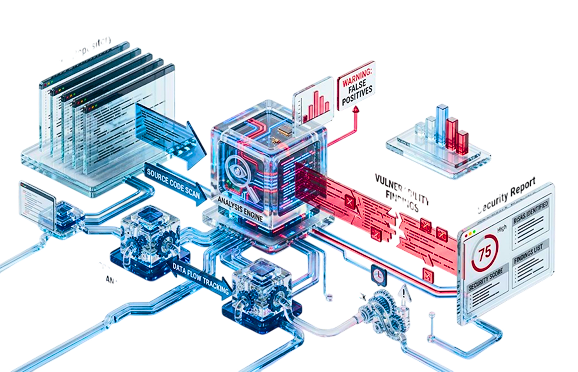
SAST illustration
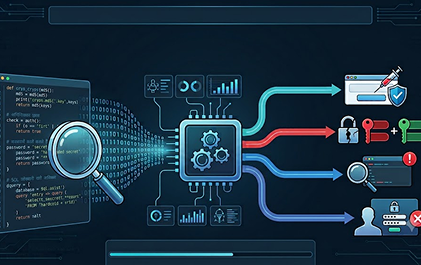
SAST security vulnerabilities in code
The problem

Insecure code ships every day.

Most security issues are introduced long before runtime — in the source code itself. Without static analysis, SQL injection, XSS, hardcoded secrets, and insecure authentication patterns quietly make their way into production. Manual code reviews simply can’t keep up with modern development velocity.
One operating picture

One platform. Every layer of security.

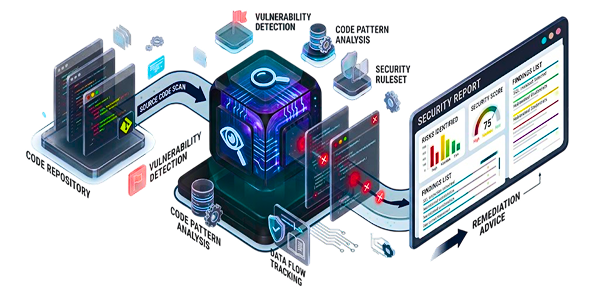
From the first line of code to production runtime, MadStack connects the signal so your team can move from “is this real?” to “it is fixed.”
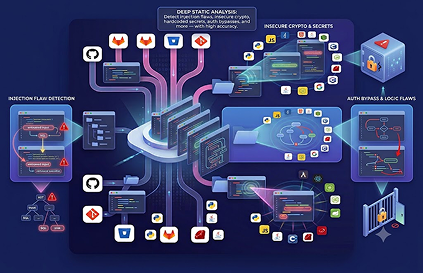
Connect your repository

Connect your repository

We automatically scan your source code across languages and frameworks the moment you connect.

Deep code analysis

Deep static analysis

We detect injection flaws, insecure crypto, hardcoded secrets, auth bypasses, and more — with high accuracy.

Prioritized findings

Get a prioritized list ranked by real-world risk

Not just severity scores — contextual risk based on exploitability and business impact.

✦ What gets detected

Findings, ranked by what matters.

Cut through noise with context-aware prioritization based on exploitability, data sensitivity, and real-world attack likelihood.

◈

Critical

SQL injection, remote code execution, and authentication bypasses with clear exploit paths.

◷ Fix within 24 hours
!

High

XSS, insecure deserialization, and hardcoded secrets found in critical paths.

◷ Prioritize this sprint
↗

Medium

Weak cryptography, missing input validation, and insecure configuration patterns.

◷ Plan the next release
Sample finding

Evidence your team can act on.

Live output from the MadStack scanner — exact file, line, vulnerability type, and recommended fix.
File
auth.controller.ts
Issue
SQL Injection
auth.controller.ts:47
// Vulnerable query
const query = SELECT * FROM users WHERE id = ${userId};
"severity": "critical",
"cwe": "CWE-89",
"issue_type": "SQL Injection",
"recommendation": "Use parameterized queries"
FAQ illustration
FAQ

Questions, answered.

MadStack SAST supports major languages including JavaScript/TypeScript, Python, Java, Go, C#, PHP, and more. We continuously expand coverage based on customer needs.

SAST analyzes your own source code for security flaws, while SCA focuses on third-party open-source dependencies. Both are complementary and work best together.

Yes. MadStack can generate pull requests with suggested fixes for many common vulnerability patterns, so your team can review and merge secure changes quickly.
More in Code

Explore More Security Topics

Dive deeper into specific areas of application security, from supply chain risks to dependency analysis and beyond.
Dependencies (SCA)

Dependencies (SCA)

Detect vulnerable open-source packages and fix them before they reach production.

Supply Chain

Supply Chain (Malware)

Detect malicious packages, scan dependencies, and stop supply chain attacks.

Deep PR Review

Deep PR Review

AI-powered code review for deeper, faster, and smarter security.

Ready when you are

Find insecure code before it ships.

SAST scan illustration