Services›Code›Outdated Software
Stay current. Stay secure.

Outdated Software Detection

Automatically detect outdated packages, frameworks, and runtimes that are no longer maintained — before they become a security risk.
Outdated Software Detection
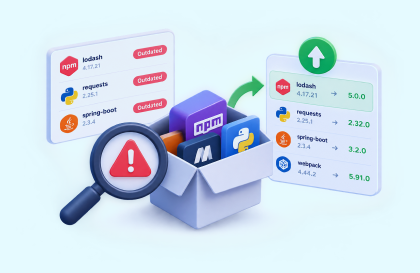
Outdated packages creating risk
The problem

Outdated software is a silent risk.

Packages that are no longer maintained stop receiving security patches. Over time, known vulnerabilities pile up, support ends, and your attack surface grows — often without anyone noticing until it’s too late. Traditional vulnerability scanners only report CVEs. They don’t tell you when a package itself is abandoned or outdated.
One operating picture

One scan. Complete visibility.

MadStack continuously monitors your dependencies and runtimes to surface outdated, abandoned, and end-of-life software — so you can upgrade before risk turns into an incident.
Detect outdated packages

Detect outdated packages

Identify libraries, frameworks, and tools that have newer stable versions available or have fallen behind recommended releases.

Flag end-of-life software

Flag end-of-life software

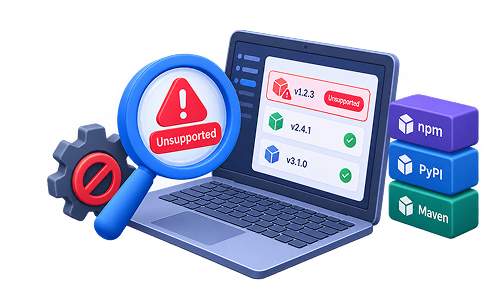
Detect packages and runtimes that are no longer maintained, have reached end-of-life, or receive no security updates.

Prioritize upgrades

Prioritize upgrades

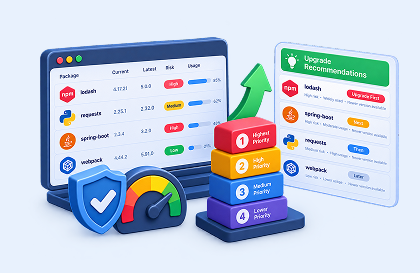
Get clear recommendations on which packages to upgrade first based on risk, usage, and available newer versions.

✦ What gets detected

Findings, ranked by what matters.

Prioritized by how outdated the software is, whether it still receives security patches, and how widely it is used in your codebase.

◈

Critical

End-of-life or completely abandoned packages that no longer receive any security updates.

◷ Upgrade immediately
!

High

Packages that are several major versions behind and missing important security or stability fixes.

◷ Plan upgrade this sprint
↗

Medium

Mildly outdated packages with newer versions available but still receiving limited support.

◷ Schedule for later
Sample finding

Evidence your team can act on.

Live output from the MadStack scanner — exact package, current version, latest version, and recommended action.
Package
express@4.17.1
Status
Outdated (Latest: 4.21.2)
package.json
{
"package": "express",
"current_version": "4.17.1",
"latest_version": "4.21.2",
"status": "Outdated",
"action": "Upgrade to 4.21.2"
}
FAQ illustration
FAQ

Questions, answered.

Vulnerability scanners look for known CVEs. Outdated Software detection focuses on packages that are behind recommended versions, abandoned, or have reached end-of-life — even if no CVE has been published yet.

Yes. We analyze your entire dependency tree, including transitive packages, so nothing outdated is missed deep in the chain.

Absolutely. You can define rules for how outdated a package can be, block end-of-life software, and automatically fail builds or PRs that introduce outdated components.
More in Code

Explore More Security Topics

Dive deeper into specific areas of application security, from source code analysis to dependency risks and beyond.
Dependencies (SCA)

Dependencies (SCA)

Detect vulnerable open-source packages and fix them before they reach production.

Licenses & SBOM

Licenses & SBOM

Generate accurate SBOMs and detect risky open-source licenses early.

Secret Detection

Secret Detection

Find exposed API keys, tokens, and credentials before they leak.

Ready when you are

Stay current. Stay secure.

Outdated Software CTA