Services›Code›MadStack Libraries
Secure by design. Ready to use.

MadStack Libraries

A carefully curated collection of battle-tested, security-hardened libraries that help developers build safer applications without reinventing the wheel or introducing unnecessary risk.
MadStack Libraries
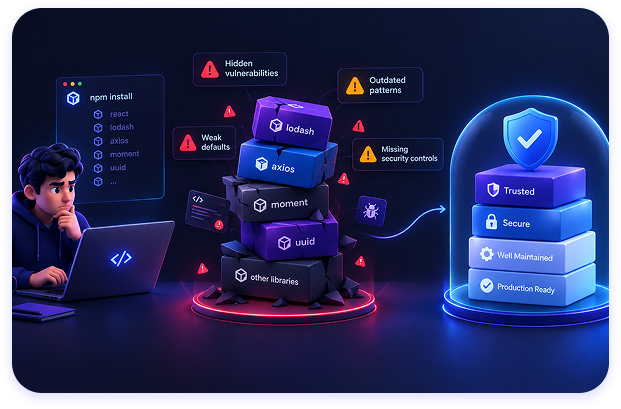
Risky vs secure libraries
The problem

Most libraries weren’t built with security in mind.

Developers often pull in popular open-source packages that solve a problem quickly — but introduce hidden risks, outdated patterns, weak defaults, or missing security controls. Writing everything from scratch is slow, expensive, and error-prone. Teams need trusted, secure building blocks they can rely on without constantly second-guessing every dependency.
One operating picture

One set of libraries. Built for security.

MadStack Libraries are designed from the ground up with modern security practices, clear documentation, and continuous maintenance — so your team can move fast without compromising safety or introducing new risk.
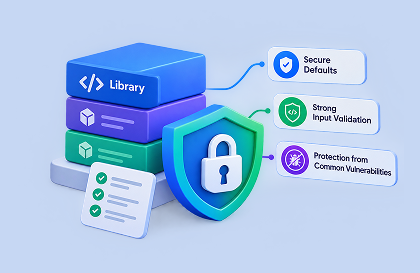
Security-first design

Security-first design

Every library is built with secure defaults, strong input validation, and protection against common vulnerabilities from day one.

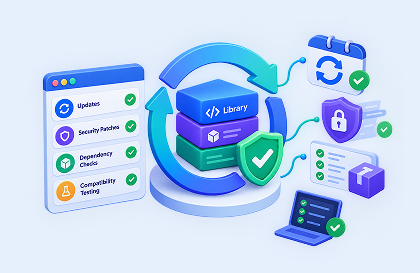
Continuously maintained

Continuously maintained

Regular updates, security patches, dependency checks, and compatibility testing keep every library production-ready.

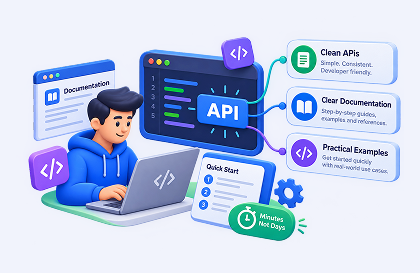
Easy to integrate

Easy to integrate

Clean APIs, clear documentation, and practical examples so developers can adopt them in minutes — not days.

✦ What you get

Libraries, ranked by what matters.

Focused on the highest-impact security and reliability needs — so teams can adopt the right building blocks with confidence and clarity.

◈

Core

Essential security and utility libraries used across most applications — the foundation every team should start with.

◷ Start here
!

Advanced

Specialized libraries for authentication, encryption, secure data handling, and advanced security patterns.

◷ Add when needed
↗

Experimental

Early-access libraries for emerging security patterns, new frameworks, and experimental approaches.

◷ Explore carefully
Sample library

Evidence your team can trust.

Live example from MadStack Libraries — package name, purpose, current status, and recommended usage.
Library
@madstack/secure-headers
Status
Production Ready
@madstack/secure-headers
{
"library": "@madstack/secure-headers",
"version": "2.4.1",
"purpose": "HTTP security headers",
"status": "Production Ready",
"action": "Recommended for all web apps"
}
FAQ illustration
FAQ

Questions, answered.

Yes. Core libraries are open source and available on public registries. Enterprise packages with additional features, priority support, and advanced capabilities are available under commercial licenses.

Every library goes through continuous security scanning, dependency checks, regular audits, and automated testing. Security patches are released as soon as issues are identified.

Yes. The libraries are designed to work across Node.js, browser environments, and common backend frameworks. Clear documentation and practical examples are provided for each supported environment.
More in Code

Explore More Security Topics

Dive deeper into specific areas of application security, from source code analysis to dependency risks and beyond.
SAST

SAST

Find and fix security flaws in your source code before they ship.

Secret Detection

Secret Detection

Find exposed API keys, tokens, and credentials before they leak.

Deep PR Review

Deep PR Review

AI-powered code review for deeper, faster, and smarter security.

Ready when you are

Build safer. Faster.

MadStack Libraries CTA