◈
Critical
Strong copyleft licenses (GPL, AGPL) used in proprietary code without proper compliance.
◷ Review & remediate
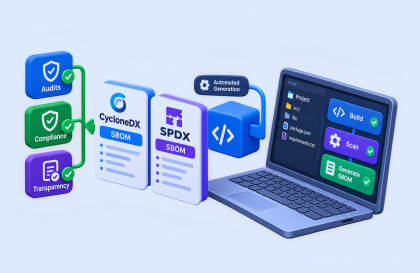
Automatically create CycloneDX and SPDX SBOMs for every project and build — ready for audits and compliance.
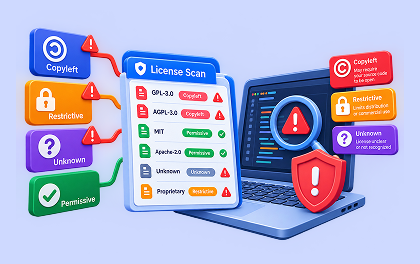
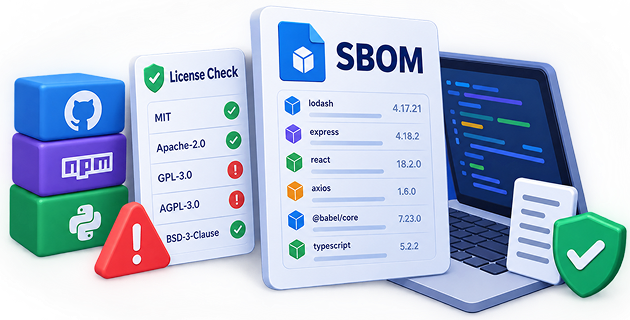
Flag copyleft, restrictive, and unknown licenses that could create legal exposure or block distribution.
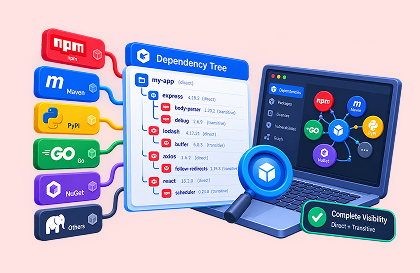
Get complete visibility into direct and transitive packages across npm, Maven, PyPI, Go, and more.
Prioritized by license risk, usage context, and potential legal or security impact — so you act on the most important issues first.
Strong copyleft licenses (GPL, AGPL) used in proprietary code without proper compliance.
Restrictive or dual-licensed packages that may limit commercial use or redistribution.
Unknown, custom, or poorly documented licenses that need clarification and tracking.
Live output from the MadStack scanner — exact package, license type, and recommended action.
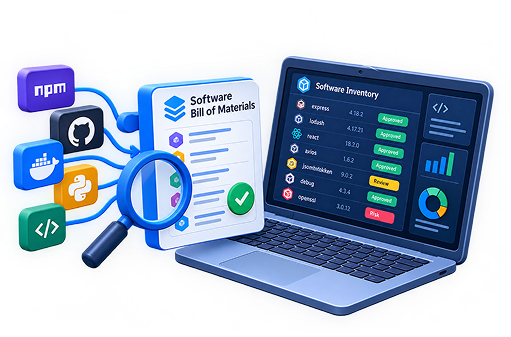
A Software Bill of Materials (SBOM) is a complete inventory of all components in your software. It helps with security, license compliance, and meeting regulatory requirements from the US Executive Order, EU regulations, and more.
We generate both CycloneDX and SPDX formats — the two most widely accepted industry standards, fully compatible with most security and compliance tools.
Yes. You can define allowed, restricted, and blocked licenses. MadStack will automatically flag any package that violates your policy during scans and in pull requests.