◈
Critical
Actively exploited CVEs with public proof-of-concept exploits and immediate exposure.
◷ Fix within 24 hours
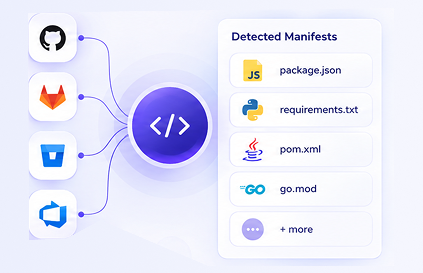
we automatically detect package manifests (package.json, requirements.txt, pom.xml, go.mod, etc.)
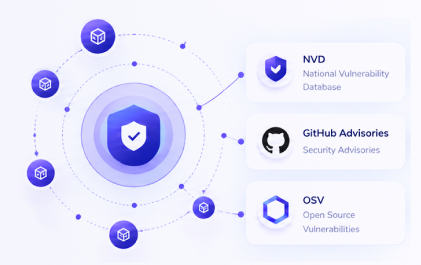
We cross-reference every direct and transitive dependency against continuously updated CVE databases (NVD, GitHub Advisories, OSV)
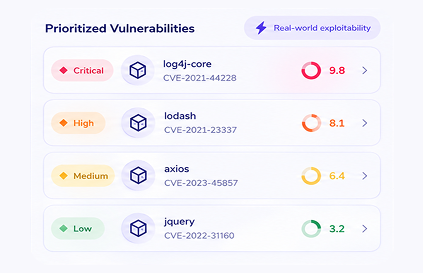
not just CVSS score
Cut through vulnerability noise with context-aware prioritization based on exploitability, business impact, and urgency.
Actively exploited CVEs with public proof-of-concept exploits and immediate exposure.
Known vulnerabilities with high CVSS scores found in direct dependencies.
Risk hidden in nested dependencies and outdated minor versions across projects.
Live output from the MadStack command line — clear package, exposure type, and the exact fix version.
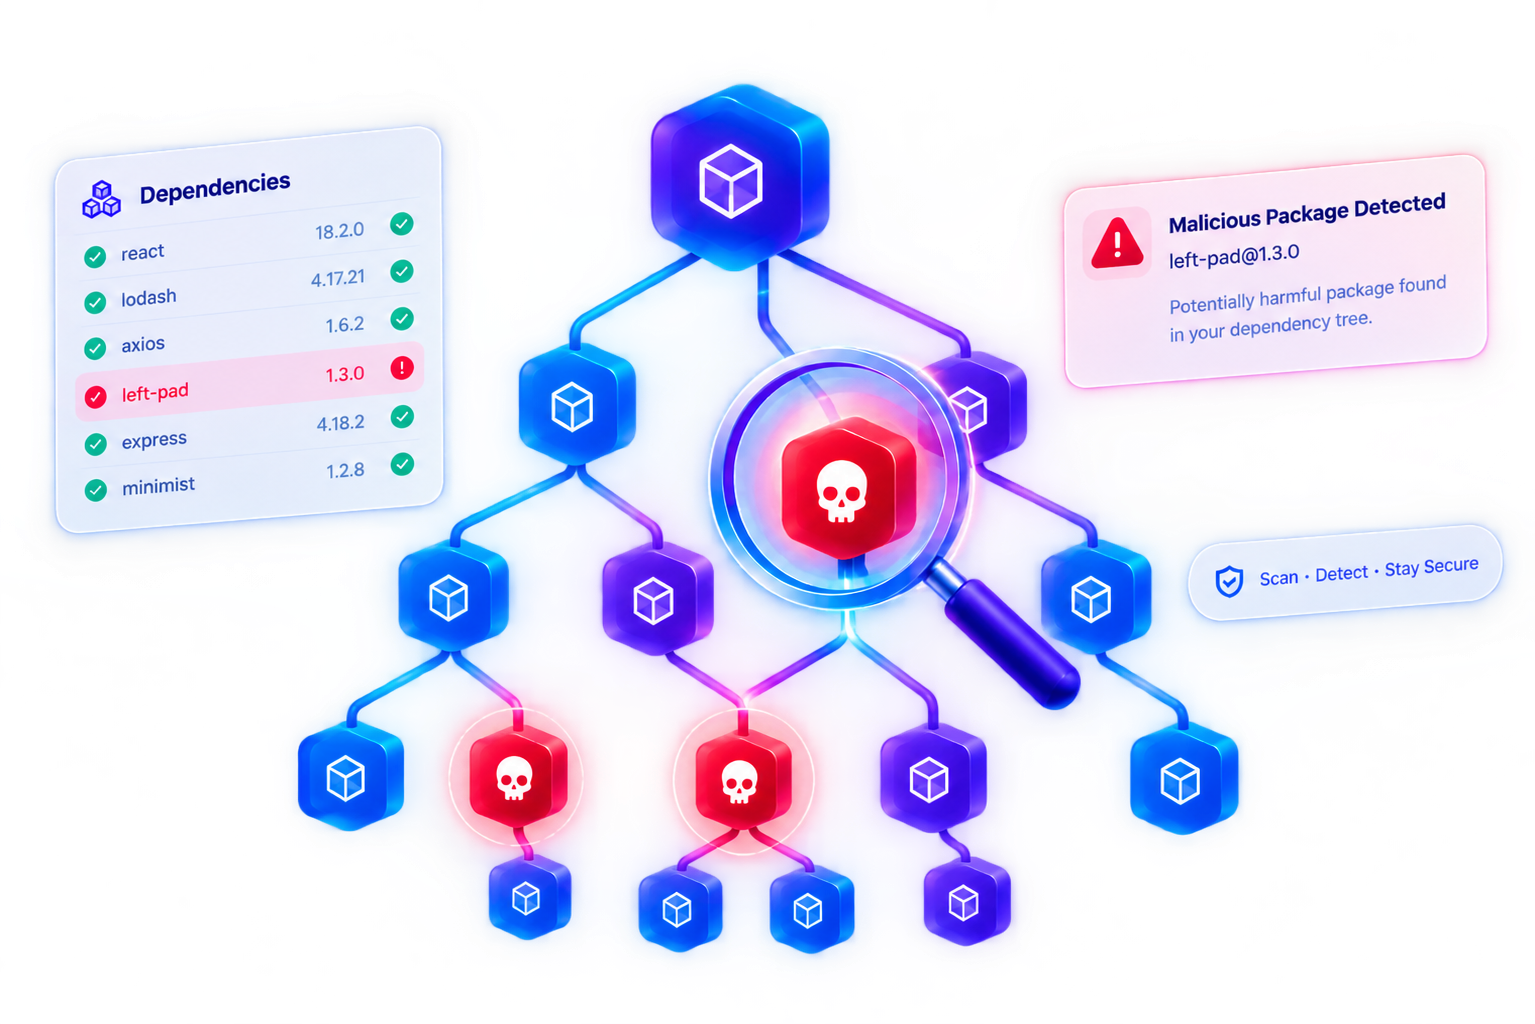
SCA analyzes both direct and transitive dependencies, uncovering hidden vulnerabilities across your entire software dependency chain and helping teams maintain secure, reliable, and compliant applications throughout development and deployment.
Our vulnerability databases are continuously updated from multiple trusted sources including NVD, GitHub Advisories, and OSV, ensuring you always have the latest threat intelligence.
Yes. MadStack can automatically generate pull requests with the recommended fixed versions, so your team can review and merge secure updates with minimal effort.