◈
Critical
Security vulnerabilities or logic errors that can break production or expose data.
◷ Block merge
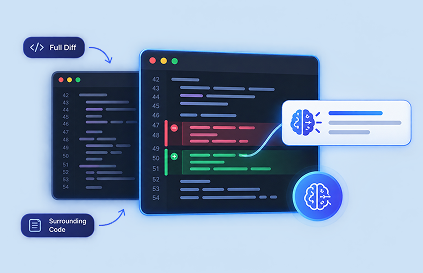
We analyze the full diff + surrounding code to grasp intent, not just the lines that changed.
Detect security flaws, logic errors, and edge cases that typical linters and bots miss.
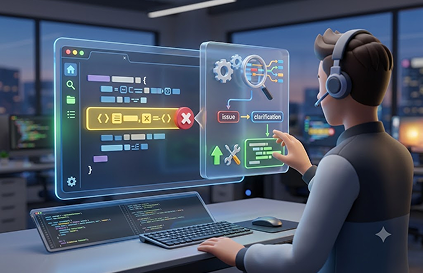
Every finding comes with clear explanation and suggested fix — so developers can act fast.
Prioritized by severity, blast radius, and confidence — so reviewers focus on the issues that truly need attention.
Security vulnerabilities or logic errors that can break production or expose data.
Potential bugs, missing edge cases, or significant maintainability risks.
Code quality issues, minor improvements, or style concerns with low impact.
Live output from MadStack Deep PR Review — exact location, issue, and recommended fix.
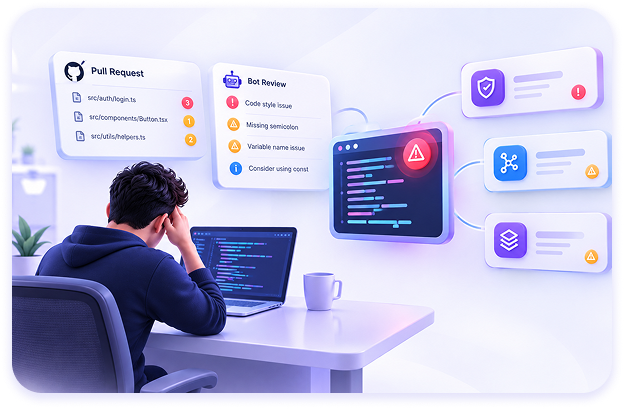
Most bots only check style and simple rules. Deep PR Review understands context, detects real security and logic issues, and explains why something is a problem.
Yes. We integrate natively with GitHub, GitLab, and Bitbucket. Reviews appear directly on the pull request.
No. Reviews complete in seconds to a couple of minutes, and findings are prioritized so teams only focus on what matters.