Services›Code›Code Quality
Clean code. Strong foundations.

Code Quality Analysis

Detect code smells, complexity, and technical debt before they slow your team down.
Code Quality Analysis
Code quality problems
The problem

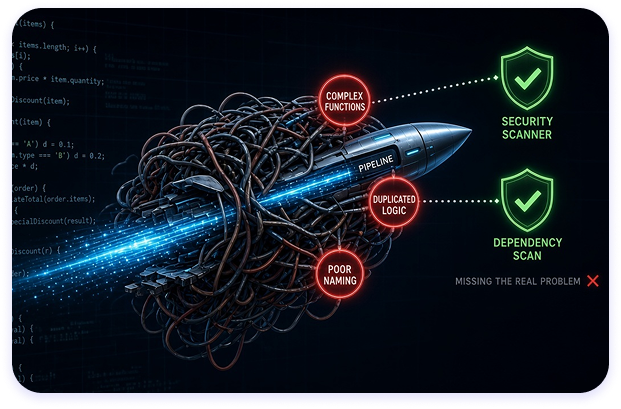
Bad code compounds silently.

Over time, complex functions, duplicated logic, and poor naming slow development, increase bugs, and make onboarding painful. Traditional tools only catch security issues — they miss the maintainability problems that quietly kill velocity.
One operating picture

One platform. Every layer of quality.

From the first line of code to production, MadStack surfaces quality issues with context so your team can fix what actually matters — not just noise.
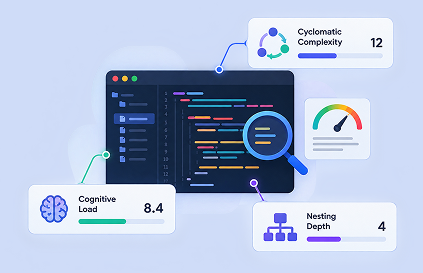
Measure complexity

Measure complexity

We analyze cyclomatic complexity, cognitive load, and nesting depth across every function and file.

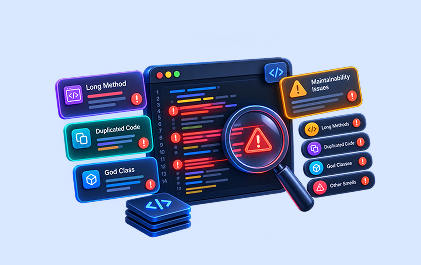
Detect code smells

Detect code smells

Identify long methods, duplicated code, god classes, and other maintainability anti-patterns.

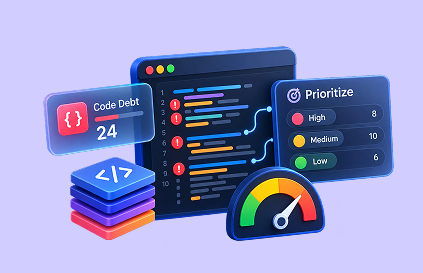
Track technical debt

Track technical debt

Quantify and prioritize debt so you know exactly where to invest engineering time.

✦ What gets detected

Findings, ranked by what matters.

Cut through noise with context-aware prioritization based on complexity impact, change frequency, and team ownership.

◈

Critical

Extremely complex or duplicated code that blocks maintainability and increases bug risk.

◷ Refactor this sprint
!

High

Long methods, deep nesting, or high cognitive complexity in frequently changed files.

◷ Plan for next sprint
↗

Medium

Naming issues, minor duplication, or moderate complexity that can wait.

◷ Monitor & improve
Sample finding

Evidence your team can act on.

Live output from the MadStack scanner — exact file, issue type, and recommended action.
File
PaymentProcessor.ts
Issue
High Cognitive Complexity
src/services/PaymentProcessor.ts
{
"file": "PaymentProcessor.ts",
"function": "processTransaction",
"issue_type": "High Cognitive Complexity",
"score": 28,
"action": "Extract methods & reduce nesting"
}
FAQ illustration
FAQ

Questions, answered.

SAST finds security vulnerabilities. Code Quality focuses on maintainability — complexity, duplication, readability, and technical debt that slow teams down over time.

Yes. We currently support JavaScript, TypeScript, Python, Java, Go, C#, and more. Analysis works on both monorepos and multi-language projects.

Absolutely. You can fail builds when complexity or debt thresholds are exceeded, so quality stays high without slowing the team down.
More in Code

Explore More Security Topics

Dive deeper into specific areas of application security, from source code analysis to dependency risks and beyond.
SAST

SAST

Find and fix security flaws in your source code before they ship.

Dependencies (SCA)

Dependencies (SCA)

Detect vulnerable open-source packages and fix them before they reach production.

Deep PR Review

Deep PR Review

AI-powered code review for deeper, faster, and smarter security.

Ready when you are

Ship cleaner code. Faster.

Code Quality CTA