◈
Critical
Publicly accessible resources, open management ports, or highly privileged IAM roles defined in code.
◷ Block & fix now
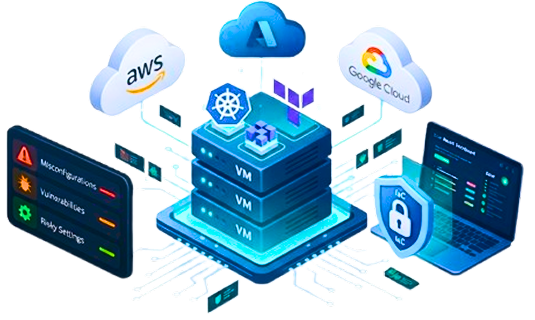
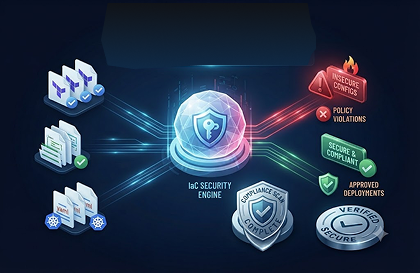
Scan Terraform, CloudFormation, Kubernetes manifests, and other IaC for insecure configurations and policy violations.
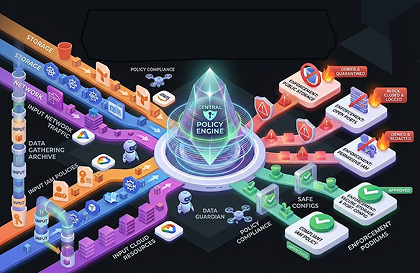
Apply custom and built-in policies to block insecure patterns like public storage, open ports, or overly permissive IAM.
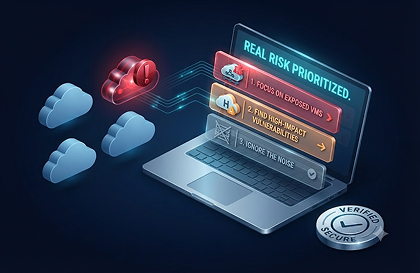
Catch issues in pull requests and CI pipelines so insecure infrastructure never gets deployed.
Prioritized by severity, potential exposure, and impact on your cloud environment — so teams fix the most critical issues first.
Publicly accessible resources, open management ports, or highly privileged IAM roles defined in code.
Missing encryption, weak network rules, or non-compliant resource configurations.
Best-practice deviations, missing tags, or non-critical policy recommendations.
Live output from the MadStack scanner — exact file, resource, issue type, and recommended fix.
We support Terraform, AWS CloudFormation, Azure Resource Manager (ARM/Bicep), Google Cloud Deployment Manager, Kubernetes manifests, Helm charts, and more.
Yes. MadStack integrates with GitHub, GitLab, and Bitbucket so you can automatically scan Infrastructure as Code changes in every pull request before they are merged.
Absolutely. You can define custom policies for encryption, network access, IAM permissions, and more. Violations can automatically fail builds or block merges.