Services›Cloud›Hardened Images
Minimal. Secure. Production-ready.

Hardened Container Images

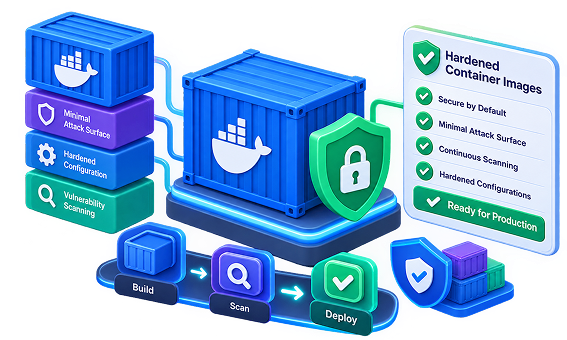
Deploy secure-by-default container images with minimal attack surface, continuous vulnerability scanning, and hardened configurations — ready for production from day one.
Hardened Container Images
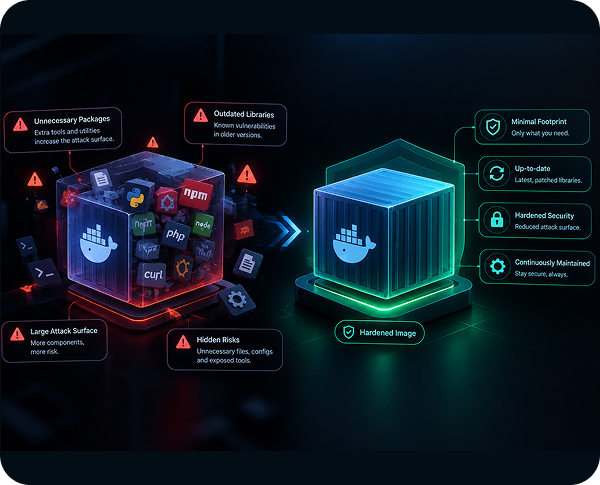
Bloated and insecure base images
The problem

Default images are rarely secure by design.

Most base images come packed with unnecessary packages, outdated libraries, and a large attack surface. Teams spend significant time hardening them manually — or worse, deploy them as-is. Hardened images solve this by providing secure, minimal, continuously maintained foundations.
One operating picture

Secure foundations. Built for production.

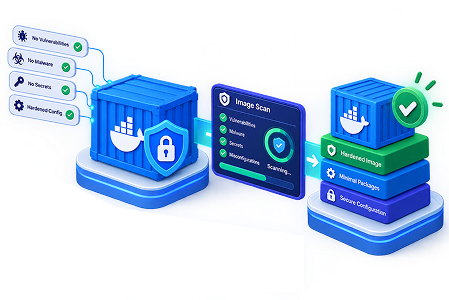
MadStack Hardened Images are minimal, continuously scanned, and designed to reduce risk from the first layer of your container stack.
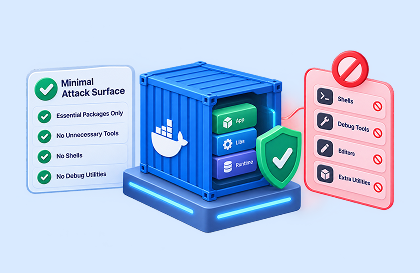
Minimal attack surface

Minimal attack surface

Only essential packages are included. No unnecessary tools, shells, or debug utilities that expand the attack surface.

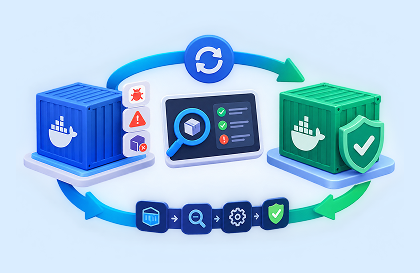
Continuously hardened

Continuously hardened

Images are regularly rebuilt, scanned, and updated to remove newly discovered vulnerabilities and outdated packages.

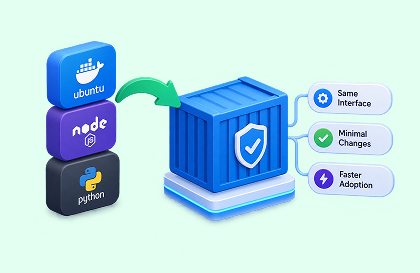
Drop-in ready

Drop-in ready

Compatible with popular base images and designed as drop-in replacements so teams can adopt them with minimal changes.

✦ What you get

Hardened by design. Ready for production.

Built with security as the default — so your applications start from a trusted, low-risk foundation.

◈

Minimal

Significantly smaller images with only the packages required to run your workload.

◷ Smaller attack surface
!

Scanned

Daily

Continuously scanned for vulnerabilities, secrets, and malware with rapid remediation.

◷ Always up to date
↗

Trusted

Signed, verifiable images that integrate cleanly into your existing CI/CD and policy workflows.

◷ Ready to adopt
Sample image

Evidence your team can trust.

Example of a MadStack Hardened Image — minimal, scanned, and ready for production use.
Image
madstack/node:20-hardened
Status
Production Ready
madstack/node:20-hardened
{
"image": "madstack/node:20-hardened",
"size": "42 MB",
"vulnerabilities": "0 Critical / 0 High",
"status": "Hardened & Signed",
"action": "Ready for production use"
}
FAQ illustration
FAQ

Questions, answered.

Hardened Images are minimal by design, continuously scanned, and regularly rebuilt to remove unnecessary packages and known vulnerabilities. They provide a secure foundation instead of requiring teams to harden standard images themselves.

Yes. Most Hardened Images are designed as drop-in replacements for popular base images (such as Node, Python, or Alpine-based images) so migration requires minimal changes.

Images are continuously monitored and rebuilt when new vulnerabilities are discovered or when upstream packages receive important security updates.
More in Cloud

Explore More Cloud Security

Dive deeper into cloud security, from container image scanning and Kubernetes to infrastructure as code.
Container Images

Container Images

Continuously scan container images for vulnerabilities, secrets, and malware.

K8s Scanning

K8s Scanning

Continuously scan Kubernetes clusters for misconfigurations and risks.

Infrastructure as Code

Infrastructure as Code

Secure Terraform, CloudFormation, and Kubernetes manifests before deployment.

Ready when you are

Start with hardened images. Build with confidence.

Hardened Images CTA