◈
Critical
Publicly exposed sensitive data, unencrypted regulated data, or overly broad access to high-value assets.
◷ Remediate now
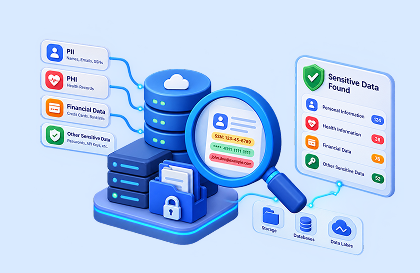
Automatically find PII, PHI, financial data, and other sensitive information across storage, databases, and data lakes.
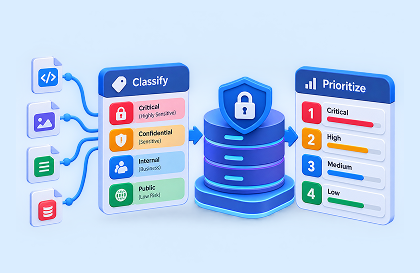
Accurately classify data by sensitivity and business impact so teams focus on the highest-risk assets first.
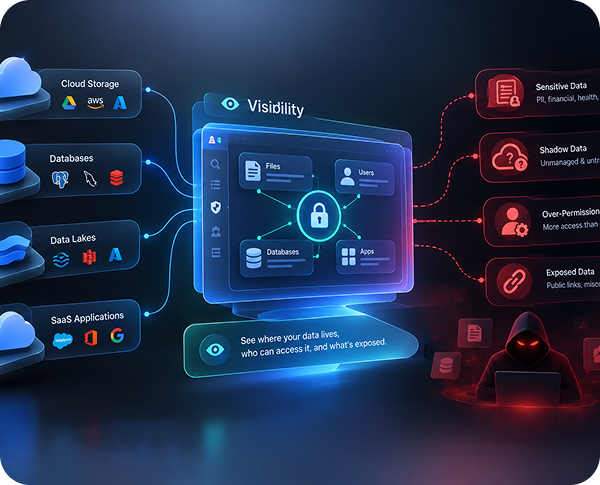
Continuously detect public exposure, excessive permissions, and risky access paths to sensitive data.
Prioritized by data sensitivity, exposure level, and access risk — so teams remediate the most dangerous data risks first.
Publicly exposed sensitive data, unencrypted regulated data, or overly broad access to high-value assets.
Excessive permissions, shadow data stores, or missing encryption on sensitive datasets.
Classification gaps, outdated access policies, or non-critical data hygiene issues.
Live output from the MadStack DSPM engine — exact data store, sensitivity, and recommended action.
We detect PII, PHI, financial data, credentials, API keys, and other regulated or business-critical information across cloud storage, databases, data lakes, and common SaaS sources.
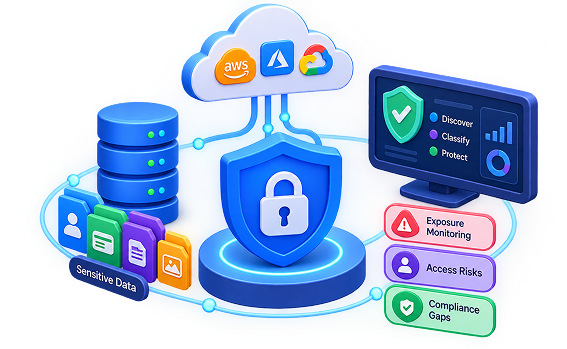
MadStack DSPM supports AWS, Microsoft Azure, and Google Cloud Platform, including multi-account and multi-region environments.
By continuously discovering and classifying sensitive data, monitoring exposure, and highlighting access risks, DSPM helps teams meet requirements for GDPR, HIPAA, PCI-DSS, and other data protection frameworks.