Services›Cloud›Container Images
Scan every image. Before it runs.

Container Image Security

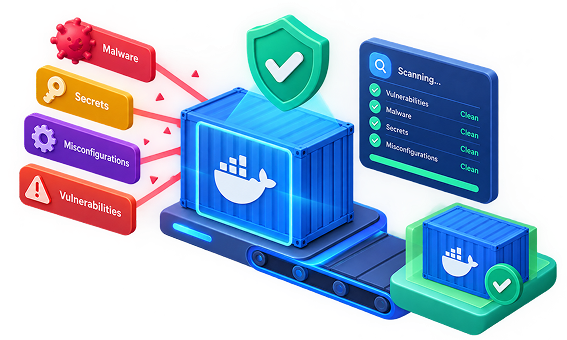
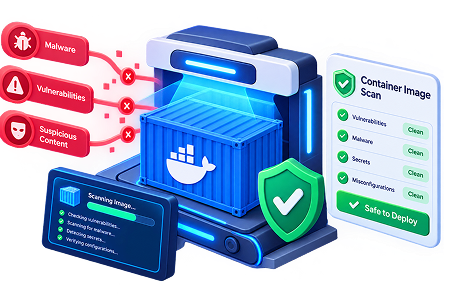
Continuously scan container images for vulnerabilities, malware, secrets, and misconfigurations — so only secure images reach production.
Container Image Security
Vulnerable container images
The problem

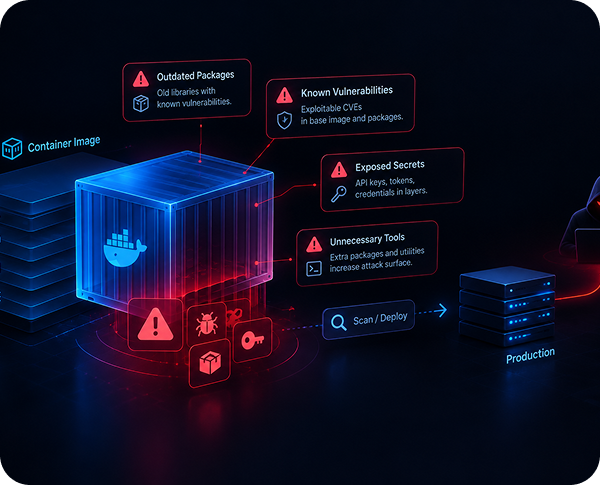
Most container images carry hidden risks.

Container images often include outdated packages, known vulnerabilities, exposed secrets, and unnecessary tools. Once these images run in production, they become an easy entry point for attackers. Scanning only after deployment is too late.
One operating picture

One scan. Complete image security.

MadStack scans container images for vulnerabilities, secrets, malware, and misconfigurations — so only trusted images are deployed.
Detect vulnerabilities

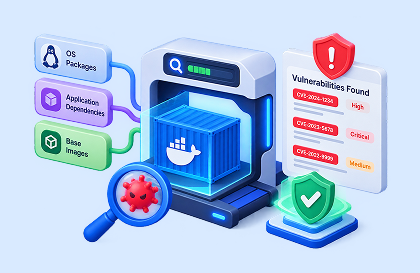
Detect vulnerabilities

Identify known CVEs in OS packages, application dependencies, and base images before they reach production.

Find secrets & malware

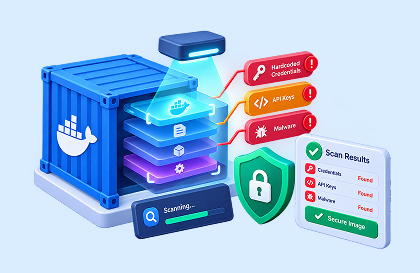
Find secrets & malware

Detect hardcoded credentials, API keys, and malicious content hidden inside container layers.

Enforce image policies

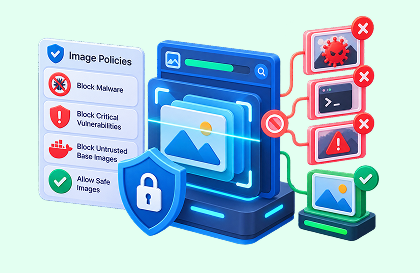
Enforce image policies

Block images that violate security policies, contain critical vulnerabilities, or use untrusted base images.

✦ What gets detected

Findings, ranked by what matters.

Prioritized by severity, exploitability, and whether the vulnerable package is actually used at runtime.

◈

Critical

Critical CVEs with known exploits, malware, or exposed secrets inside the image.

◷ Block immediately
!

High

High-severity vulnerabilities in base images or application dependencies.

◷ Fix before deploy
↗

Medium

27

Medium-severity issues, outdated packages, or non-critical configuration findings.

◷ Plan & update
Sample finding

Evidence your team can act on.

Live output from the MadStack scanner — exact image, vulnerability, and recommended fix.
Image
node:18-alpine
Issue
CVE-2024-21626 (Critical)
registry.example.com/app:1.4.2
{
"image": "node:18-alpine",
"cve": "CVE-2024-21626",
"severity": "Critical",
"package": "runc",
"action": "Upgrade base image to node:20-alpine"
}
FAQ illustration
FAQ

Questions, answered.

We support Docker Hub, Amazon ECR, Google Artifact Registry, Azure Container Registry, GitHub Container Registry, and private registries.

Best practice is to scan images during the CI/CD pipeline, before they are pushed to the registry, and continuously monitor images already in use.

Yes. You can define policies that automatically fail builds or block deployments when critical or high-severity vulnerabilities are found.
More in Cloud

Explore More Cloud Security

Dive deeper into cloud security, from Kubernetes and infrastructure as code to virtual machines and misconfigurations.
K8s Scanning

K8s Scanning

Continuously scan Kubernetes clusters for misconfigurations and risks.

Infrastructure as Code

Infrastructure as Code

Secure Terraform, CloudFormation, and Kubernetes manifests before deployment.

Cloud Misconfigurations

Cloud Misconfigurations

Detect insecure cloud configurations before they become breaches.

Ready when you are

Secure every container image. Before it runs.

Container Images CTA