◈
Critical
Publicly exposed storage, open databases, or admin roles with excessive permissions that can lead to full account takeover.
◷ Fix immediately
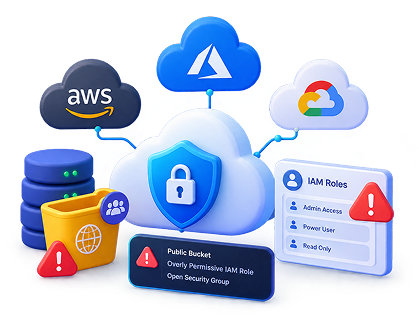
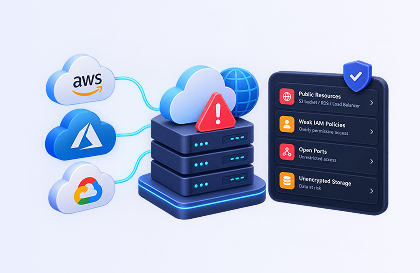
Continuously scan AWS, Azure, and GCP for public resources, weak IAM policies, open ports, and unencrypted storage.
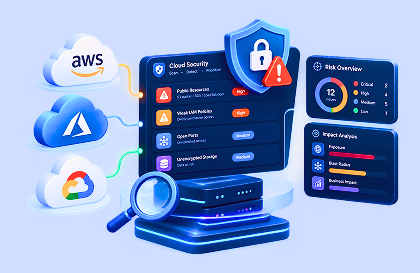
Focus on the misconfigurations that actually matter — based on exposure, blast radius, and business impact.
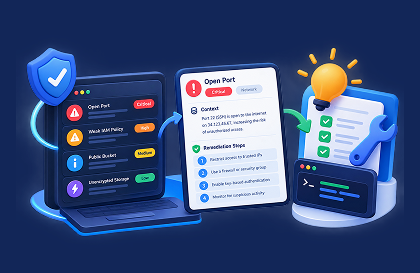
Every finding comes with context, severity, and step-by-step remediation so your team can fix issues fast.
Prioritized by exposure level, potential blast radius, and whether the resource is publicly accessible or holds sensitive data.
Publicly exposed storage, open databases, or admin roles with excessive permissions that can lead to full account takeover.
Overly permissive security groups, missing encryption, or weak network controls that significantly increase attack surface.
Logging disabled, outdated configurations, or non-critical resources with moderate exposure risk.
Live output from the MadStack scanner — exact resource, misconfiguration type, and recommended fix.
We currently support AWS, Microsoft Azure, and Google Cloud Platform. Multi-account and multi-region scanning is fully supported across all three.
You can run continuous monitoring or scheduled scans. Most teams enable continuous scanning so new misconfigurations are detected within minutes of being introduced.
No. We prioritize findings based on real exposure and business impact, and provide clear context so teams only act on issues that actually matter.