Services›Attack›Pentests
Expert-led. Real attacks. Clear risk.

Penetration Testing

Expert-led penetration testing that simulates real-world attacks on your applications, infrastructure, and cloud environments — so you understand what’s actually exploitable and how to fix it.
Penetration Testing
Why automated scans are not enough
The problem

Scanners find issues. Attackers find paths.

Automated tools surface vulnerabilities, but they rarely show how those issues chain into real attacks. Business logic flaws, misconfigurations, and creative exploit paths often remain hidden. Expert-led penetration testing reveals what scanners miss and validates true risk.
One operating picture

Expert-led testing. Actionable risk.

MadStack penetration testing combines skilled attackers with clear reporting so your team understands real impact and prioritizes the right fixes.
Cover the full attack surface

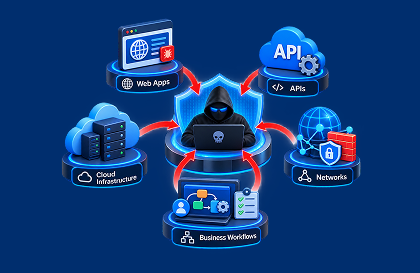
Cover the full attack surface

Test web apps, APIs, cloud infrastructure, networks, and critical business workflows under realistic attack conditions.

Prove real exploitability

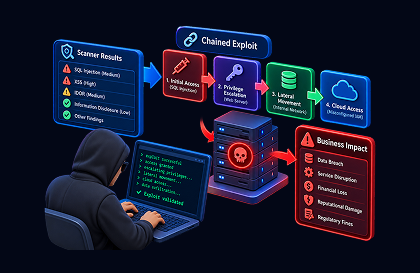
Prove real exploitability

Go beyond scanner output. Validate which issues can actually be chained into meaningful attacks and business impact.

Clear, actionable reporting

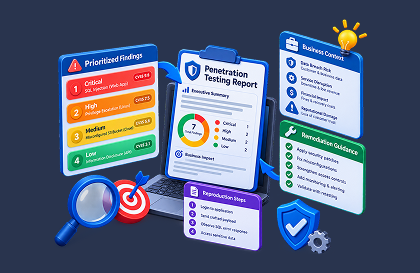
Clear, actionable reporting

Receive prioritized findings with business context, reproduction steps, and practical remediation guidance your team can act on.

✦ What gets detected

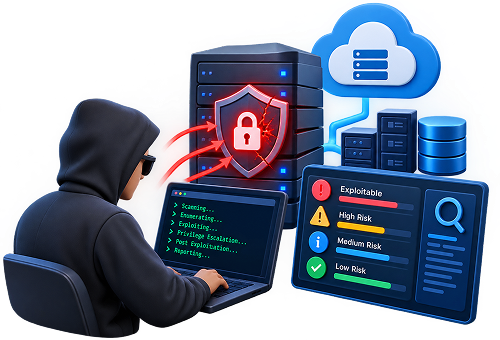
Findings, ranked by what matters.

Prioritized by exploitability, business impact, and potential blast radius — so teams fix the issues attackers would actually use first.

◈

Critical

Fully exploitable paths that can lead to data compromise, account takeover, or significant system access.

◷ Fix immediately
!

High

High-confidence attack paths that can be chained with other findings or used with moderate effort.

◷ Remediate this sprint
↗

Medium

Issues that expand attack surface or become more serious when combined with other weaknesses.

◷ Plan & harden
Sample finding

Evidence your team can act on.

Example output from an expert-led pentest — exact target, attack path, and recommended remediation.
Target
app.example.com
Issue
IDOR → Data Exposure
Expert-led Pentest · Application
{
"target": "app.example.com",
"attack_path": "IDOR → Unauthorized Data Access",
"severity": "Critical",
"exploitable": "true",
"action": "Enforce object-level authorization checks"
}
FAQ illustration
FAQ

Questions, answered.

We test web applications, APIs, mobile backends, cloud infrastructure, internal networks, and critical business workflows. Scope is tailored to your environment and risk priorities.

Automated scanners find known issues. Expert-led pentests validate exploitability, uncover business logic flaws, and show how multiple weaknesses can be chained into real attack paths.

You receive a clear report with prioritized findings, business impact context, reproduction steps, and practical remediation guidance. Optional retesting can confirm that critical issues have been fixed.
More in Attack

Explore More Attack Services

Dive deeper into offensive security — from continuous testing and red teaming to attack surface visibility.
Continuous Pentests

Continuous Pentests

Ongoing attack simulation so new risks are found as your environment changes.

Red Teaming

Red Teaming

Full-scope adversary simulation to test detection and response capabilities.

Attack Surface Management

Attack Surface Management

Continuously discover and monitor your external attack surface.

Ready when you are

Know your real risk. Fix what matters.

Pentests CTA