◈
Critical
SQL injection, authentication bypass, or remote code execution in running applications.
◷ Fix immediately
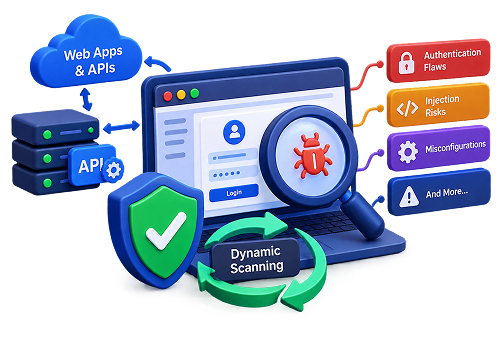
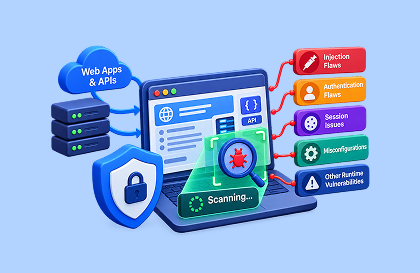
Test live web apps and APIs for injection, authentication flaws, session issues, and other runtime vulnerabilities.
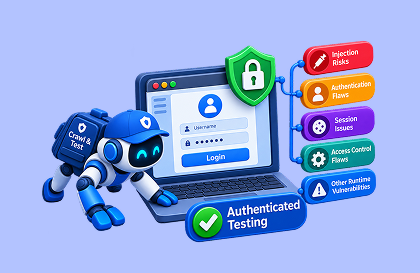
Crawl and test authenticated areas of the application to uncover risks that only appear after login.
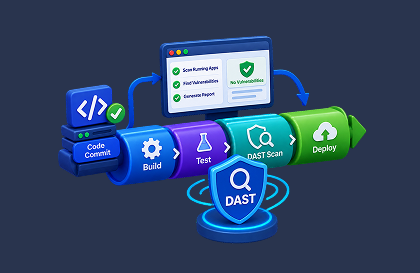
Run DAST scans as part of your pipeline so new runtime issues are caught before release.
Prioritized by severity, exploitability, and potential impact on users and data — so teams fix the most dangerous runtime issues first.
SQL injection, authentication bypass, or remote code execution in running applications.
XSS, insecure session handling, or sensitive data exposure through APIs.
Misconfigured headers, information disclosure, or less severe input validation issues.
Live output from the MadStack DAST engine — exact endpoint, issue type, and recommended fix.
SAST analyzes source code without running the application. DAST tests the running application from the outside, the way an attacker would, and finds issues that only appear at runtime.
Yes. MadStack DAST supports authenticated scanning so it can crawl and test areas that require login, sessions, or tokens.
Best practice is to run DAST regularly — ideally on every major release or continuously in CI/CD — so new runtime vulnerabilities are caught quickly as the application changes.