◈
Critical
Fully exploitable paths that can lead to data access, privilege escalation, or system compromise.
◷ Fix immediately
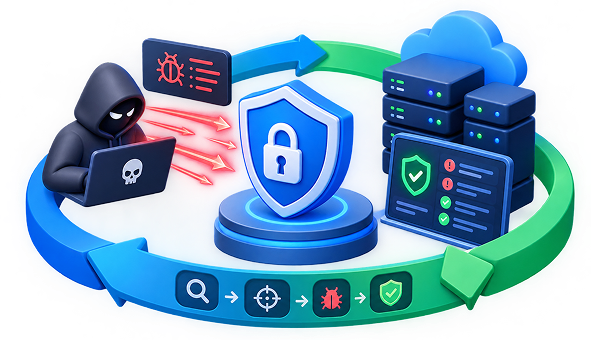
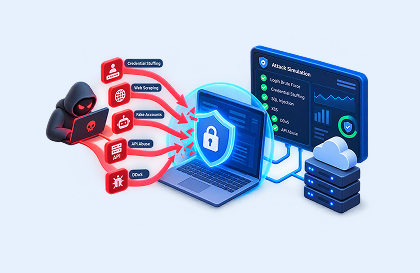
Continuously run attack scenarios that mirror real adversary techniques against your applications and infrastructure.
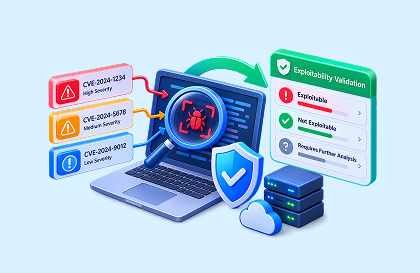
Go beyond vulnerability reports. Confirm which findings are actually exploitable in your environment.
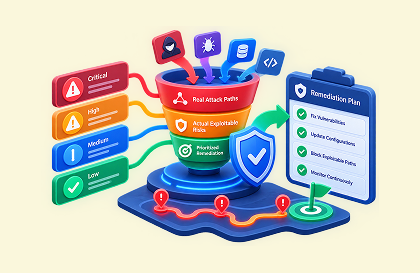
Focus remediation on the issues that create actual attack paths — not just theoretical vulnerabilities.
Prioritized by exploitability, business impact, and whether a real attack path exists — so teams fix what attackers would actually use.
Fully exploitable paths that can lead to data access, privilege escalation, or system compromise.
High-confidence attack paths that require limited effort to exploit or chain with other findings.
Issues that increase attack surface or could become exploitable under specific conditions.
Live output from continuous testing — exact target, attack path, and recommended remediation.
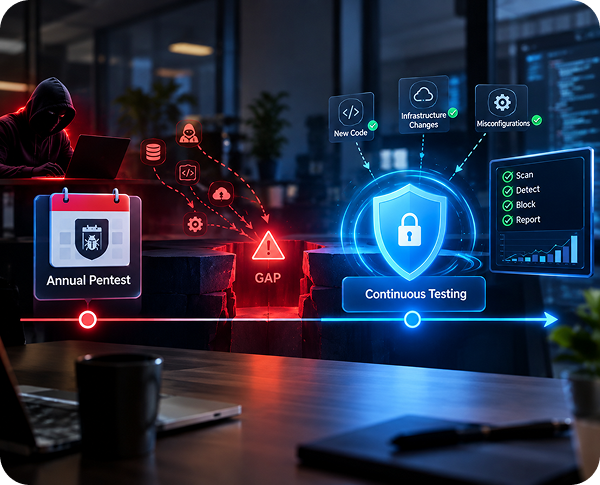
Traditional pentests are point-in-time assessments. Continuous pentesting runs ongoing attack simulations as your environment changes, so new vulnerabilities and attack paths are discovered quickly instead of waiting for the next annual test.
It complements it. Continuous testing provides ongoing coverage and validates exploitability at scale, while expert-led manual testing is still valuable for deep, creative, and business-logic focused assessments.
We support web applications, APIs, cloud infrastructure, and external attack surfaces. Scope and frequency can be tailored to your risk profile and change velocity.