◈
Critical
Publicly exposed critical systems, open management ports, or high-value assets with known weaknesses.
◷ Secure immediately
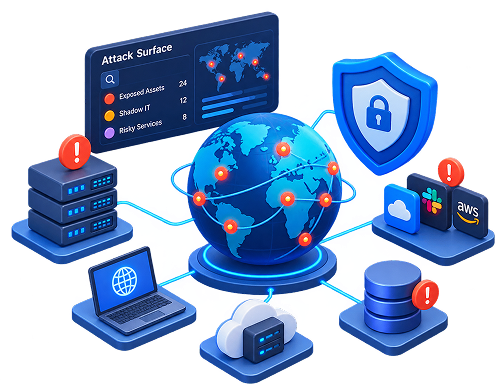
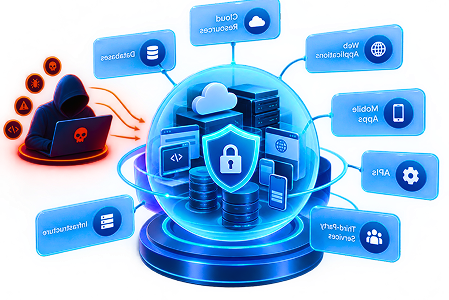
Automatically find domains, subdomains, IPs, cloud services, and exposed applications across your organization.
Track new assets, disappearing services, and configuration changes as your attack surface evolves.
Focus on exposed services, high-value assets, and changes that meaningfully increase attacker opportunity.
Prioritized by exposure, asset criticality, and potential attacker value — so teams reduce the most dangerous surface first.
Publicly exposed critical systems, open management ports, or high-value assets with known weaknesses.
New or unowned assets, exposed services, or significant changes that expand attacker opportunity.
Informational findings, low-risk exposures, or assets that need ownership and hygiene improvements.
Live output from MadStack ASM — exact asset, exposure type, and recommended action.
We continuously discover domains, subdomains, IP addresses, cloud services, exposed applications, open ports, and related external assets tied to your organization.
Attack surfaces change constantly. ASM continuously monitors for new, changed, and disappearing assets so your inventory stays accurate instead of becoming outdated after a single scan.
Yes. By discovering unknown or unowned assets and flagging unexpected exposures, ASM helps teams identify shadow IT and bring it under proper ownership and control.