Services›Attack›API Scanning
Secure every API. Continuously.

API Security Scanning

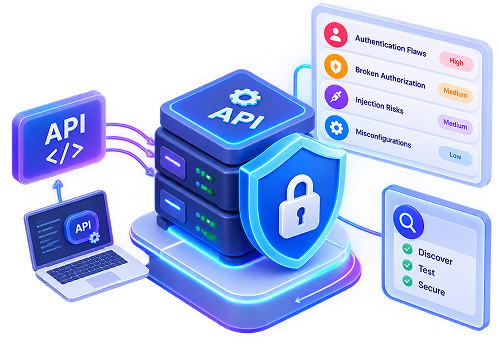
Continuously discover, test, and secure your APIs. Detect authentication flaws, broken authorization, injection risks, and misconfigurations before attackers exploit them.
API Security Scanning
APIs are the new attack surface
The problem

APIs are the new attack surface.

Modern applications expose more APIs than ever — internal, external, and third-party. Many lack proper authentication, authorization, and input validation. Shadow APIs and undocumented endpoints create blind spots that scanners and traditional testing often miss.
One operating picture

One scan. Complete API visibility.

MadStack continuously discovers and tests your APIs so security risks are found early — across REST, GraphQL, and other interfaces.
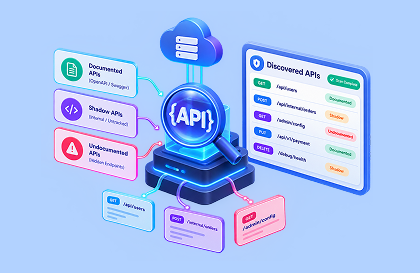
Discover all APIs

Discover all APIs

Automatically find documented and shadow APIs across your environment, including undocumented endpoints.

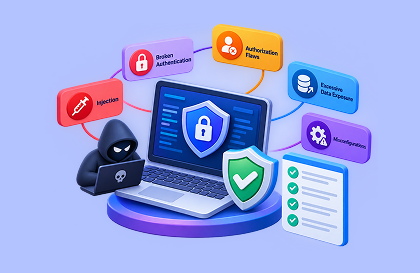
Test for real risks

Test for real risks

Detect broken authentication, authorization flaws, injection, excessive data exposure, and misconfigurations.

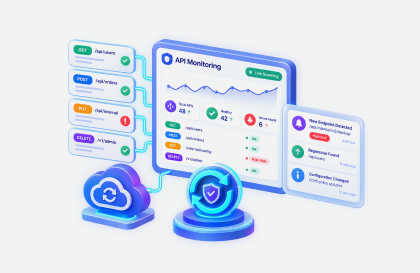
Continuously monitor

Continuously monitor

Keep scanning as APIs change so new endpoints and regressions are caught quickly.

✦ What gets detected

Findings, ranked by what matters.

Prioritized by exploitability, data sensitivity, and potential business impact — so teams fix the most dangerous API risks first.

◈

Critical

Broken auth, IDOR leading to data access, or injectable endpoints with high impact.

◷ Fix immediately
!

High

Excessive data exposure, weak rate limiting, or insecure object-level authorization.

◷ Remediate this sprint
↗

Medium

Missing security headers, verbose errors, or non-critical input validation gaps.

◷ Plan & harden
Sample finding

Evidence your team can act on.

Live output from the MadStack API scanner — exact endpoint, issue type, and recommended fix.
Endpoint
GET /api/v1/users/{id}
Issue
Broken Object Level Auth (IDOR)
API Scan · Production
{
"endpoint": "GET /api/v1/users/{id}",
"issue_type": "Broken Object Level Authorization (IDOR)",
"severity": "Critical",
"exploitable": "true",
"action": "Enforce object-level authorization checks"
}
FAQ illustration
FAQ

Questions, answered.

We support REST APIs, GraphQL, and common API gateways. Scans can cover both public and authenticated endpoints.

Yes. MadStack discovers APIs from traffic, specs, and runtime behavior — including endpoints that are not listed in your documentation.

You can run API scans in your pipeline so new endpoints and regressions are tested before they reach production.
More in Attack

Explore More Attack Services

Dive deeper into offensive security — from DAST and penetration testing to continuous testing and attack surface management.
DAST

DAST

Continuously test running web applications for runtime vulnerabilities.

Pentests

Pentests

Expert-led penetration testing that proves real exploitability and business impact.

Continuous Pentests

Continuous Pentests

Ongoing attack simulation so new risks are found as your environment changes.

Ready when you are

Secure every API. Before it’s exploited.

API Scanning CTA